
Cyberduck Alternative: Administered File Access With Central Permissions and Audit
MyWorkDrive gives IT a single gateway that publishes the organization's own file servers, NAS, SharePoint, OneDrive, Azure, and S3 to staff over HTTPS. Every request is authorized against existing permissions at the server, and every action is written to one central audit record.
Open-source transfer and mounting clients are capable tools for individual technical work. What they do not provide is an administrative layer. The connections, the saved credentials, and the record of activity all live on each user's own machine, outside the controls a security review examines.

Trusted by Organizations Worldwide


Administration, Security, and Compliance Comparison
How an administered access gateway and a per-user transfer client differ on the controls a security review examines.
| Control |
|
Open-source transfer and mounting client
|
|---|---|---|
| Administration | Central gateway configured and controlled by IT | Configured individually on each machine by its user |
| Connection definitions | Shares published centrally by administrators and presented by group membership | Bookmarks created and held locally by each user |
| Credentials on user devices | None. Users authenticate to the gateway with directory credentials and MFA | Saved locally in bookmarks or the system keychain |
| Where authorization is decided | At the gateway, against existing NTFS ACLs and directory groups | By the storage, using the credential the user configured |
| Identity and single sign-on | Active Directory, Entra ID, SAML, ADFS, Okta, with MFA and Duo | Per-protocol authentication, including SSH keys and client certificates |
| Remote access to internal file servers | HTTPS on port 443, or an outbound-only tunnel with no published server | Requires a VPN or a transfer protocol published to the internet |
| Audit record | Central server-side log of logins, file activity, and shares, exported to syslog and SIEM | No central record. Activity is local to each installation |
| Data loss prevention controls | Device approval and blocking, session management, block download, and watermarking enforced at the gateway | Not an administrative function of the client |
| External sharing | Expiring, password-protected links with download restriction, watermarking, and administrator revocation | Signed or temporary storage URLs generated by the user |
| Offboarding | Disabling the directory account ends access across every client immediately | Requires reaching the device to remove saved bookmarks and keys |
| Client coverage | Mapped drive on Windows and macOS, web browser, iOS, and Android | Windows and macOS desktops |
| Licensing basis | Named users who sign in, tracked over a rolling 30 day period and reassignable | Free client, with a paid per-seat key for the mounting product |
Centrally Administered Access to the Organization's Own Storage
Five capabilities separate an administered access layer from a client each user configures independently.
Administration
Shares published by IT rather than configured per user
Administrators define at the gateway which shares exist and which directory groups may reach them. Staff sign in and see exactly what their group membership allows, with no connection details to distribute and nothing to configure on the device.
No distributed estate of hand-built connections to inventory, support, or clean up after someone leaves.
Credentials
No saved connections or keys held on user devices
Users authenticate against Active Directory, Entra ID, SAML, ADFS, or Okta with MFA and Duo, and the gateway holds the connection to the storage. No protocol credential, SSH key, or access key is written to a laptop or a home machine.
A lost or stolen device carries no reusable path to the file server, and disabling the directory account ends access everywhere at once.
Permissions
Existing NTFS permissions enforced at the gateway
Every request is evaluated against existing NTFS ACLs and directory group membership before any data moves, on the server, where the decision cannot be influenced by software running on the user's machine. Access is never governed by what a shared service account happens to reach.
One authoritative permission set, already maintained on the file server, governs every client and every session.
Audit and compliance
One central record of file and login activity
Logins, file opens, edits, downloads, and share activity are recorded centrally at the gateway and exported to syslog and SIEM, covering every user and every client type from a single source rather than leaving no organizational trace.
Access evidence for HIPAA, CMMC, FINRA, FERPA, and GDPR assessments is produced from one server-side record.
Remote access
File server access over HTTPS with no VPN
MyWorkDrive publishes existing shares on port 443 from a server the organization already runs, with an outbound-only tunnel option for environments that will not publish a server at all. No SMB, SFTP, or FTP service is exposed to the internet.
Remote file access without a VPN client to license and support, and without a transfer protocol on the perimeter.
Administered File Access Without a VPN Project
No VPN, No Migration
Existing file servers, SharePoint, OneDrive, Azure, and S3 are published over HTTPS on port 443 where they are. No VPN client to roll out and no SMB exposed to the internet.
Existing NTFS Permissions Enforced
Native Active Directory and Entra ID integration, with authorization decided at the server. No storage credentials on user devices and no second permission model.
Lower Cost of Ownership
$5 per user per month billed annually, licensed on named users who sign in over a rolling 30 day period. No VPN licensing to add. Support included with every plan.
Requirements That Call for a Protocol Transfer Client
Scope of an administered access gateway
Moving build artifacts into an object storage bucket, connecting to a third-party SFTP host a partner operates, and inspecting a web server over FTPS are transfer client tasks, and an open-source client built for them is well suited and widely used for exactly that work. Those cases involve a single technical user, a credential that user owns, and storage outside the organization's own permission model. MyWorkDrive is not a protocol client and does not connect to arbitrary SFTP or FTP hosts. It publishes the organization's own file estate to staff under the permissions and identity already in place.
Your organization's storage
StaffDesktop, browser, and mobile
MyWorkDrive gateway
Directory + MFANTFS permissionsCentral audit
File servers and NAS
SharePoint and OneDrive
Azure and S3
Published by IT under existing permissions
External endpoints
One technical userWith a credential they own
Transfer client
Saved bookmarksLocal keys
Partner SFTP host
Build artifact bucket
Web server over FTPS
Outside the organization's permission model
Secure File Access FAQ
Can MyWorkDrive replace Cyberduck?

Where the requirement is giving staff administered access to the organization's own file servers, SharePoint, or cloud storage, yes, and it adds the central permission enforcement, auditing, and offboarding that a per-user client cannot provide. Where the requirement is ad hoc technical access to an external SFTP, FTP, or object storage endpoint, a protocol transfer client remains the correct tool.
What are the risks of staff using a file transfer client to reach company file shares?
Connections and credentials are created and stored on each machine outside IT control. Access is governed by whatever the configured account can reach rather than by the user's directory permissions. No central record of file activity exists for an audit, and offboarding depends on physically reaching the device to remove saved bookmarks and keys.
Does MyWorkDrive mount storage as a drive letter?
Yes. A mapped drive client for Windows and macOS presents connected shares as a drive letter, with files streamed on demand. The difference is administrative: the shares are published centrally, and every request is authorized at the server against existing permissions rather than by a connection the user built.
Are storage credentials stored on user devices?
No. Users authenticate to the gateway with directory credentials and MFA, and the gateway holds the connection to the storage. A lost or stolen device carries no reusable connection to the file server, and access ends when the directory account is disabled.
How does MyWorkDrive enforce permissions?
Every request is evaluated at the gateway against existing NTFS ACLs and Active Directory or Entra ID group membership. No permission structure is rebuilt, and the decision is made on the server rather than by software running on the user's device.
How long does MyWorkDrive deployment take?
MyWorkDrive installs as a single role on an existing Windows Server using IIS, with shares connected in hours. No data migration, no re-permissioning, and no change to how staff file documents.
Security You Can Prove
With MyWorkDrive, authentication and authorization stay anchored in your directory and your NTFS. No vendor keys to rotate for at-rest copies you don’t control, and no third-party repository to certify, making attestations simpler for regulated workloads.
Data Loss Prevention
(Block downloads, disable copy/paste, watermarking, device approvals)
Learn more
What our users are saying
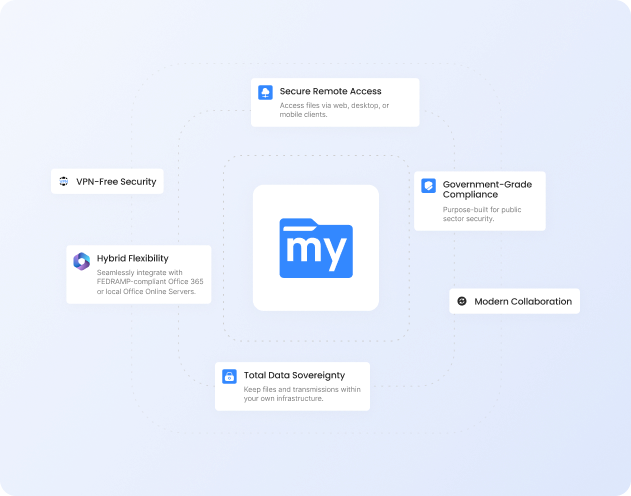
 Industry-leading secure remote file access solution
We have determined that MyWorkDrive software is essential to the Government’s requirements and market research indicates that other companies’ similar products do not meet or cannot be modified to meet the agency’s needs.
We conducted annual market research in January 2025 by comparing two competitors, ShareFile and Dropbox.
However, neither of these companies provides us with the necessary capabilities required to allow us to utilize the existing infrastructure, maintain stringent control over their data, and integrate with current enterprise security and authentication protocols.
These companies software do not provide real-time collaboration capabilities, does not eliminate Virtual Private Network (VPN) security risks nor prevent lateral network access.
Due to the inabilities noted, we have determined that MyWorkDrive software is essential to the Government’s requirements and market research indicates that other companies’ similar products do not meet or cannot be modified to meet the agency’s needs.
MyWorkDrive is the most network secure compatible software application capable of eliminating VPN security risks and preventing lateral network access…
…Therefore, it is in the Government’s best interest to procure MyWorkDrive software.
Undisclosed Government Agency
See More Reviews



See the MyWorkDrive Advantage for Yourself
Book a personalized demo or start your free trial today